A BuiltWith alternative does not need to reproduce a
global historical database to be useful. If your CRM already contains
company domains, a focused API can fetch each public website, identify
visible technology signals, and return structured evidence while the
data is still fresh.
That narrower job matters. A sales team may need to know whether a
new account appears to use Shopify, WordPress, HubSpot, Stripe, Next.js
or Cloudflare before routing it. A migration agency may want to flag
WooCommerce stores. A SaaS vendor may prioritize sites using an
integration it supports. None of those workflows automatically require
millions of pre-indexed domains.
This guide shows how to build that workflow with Node.js and the CMS
Checker & Website Technology Detector API. You will make a
lookup, interpret confidence and evidence, normalize the result for a
CRM, process a small batch, and decide when a real-time checker is the
wrong tool.
Fast path: The Basic plan includes 50 requests per
month. Use them to test five known sites from each segment before
changing any CRM automation.
By Faraz Ahmad · StadiaSoft · September 18, 2026 · 14-minute
read
What the keyword
data says about buyer intent
This article targets a specific search rather than a guessed topic.
On September 18, 2026, Ahrefs reported 200 monthly US searches for
builtwith alternative, Keyword Difficulty 1, $4.00 CPC and
traffic potential of 250 visits. Semrush reported 480 US searches, 3%
difficulty and $6.17 CPC.
The tools use different datasets, so their absolute volumes differ.
They agree on the useful part: the query has commercial value and
unusually low ranking difficulty. The current search results also reveal
a gap. Most ranking pages are product comparisons, browser tools or
vendor landing pages. Few explain how to enrich domains programmatically
while preserving the evidence behind a detection.
The broader phrase CMS detector has more volume, but it
is less precise. Search results sometimes mix website content-management
systems with the Compact Muon Solenoid detector used in particle
physics. BuiltWith alternative is the better primary topic
for a developer-facing, commercial workflow. CMS detector
and website technology checker remain useful secondary
phrases.
Decide
whether you need a lookup, database or browser extension
The category contains three different products. Choosing the wrong
one creates unrealistic expectations.
| Requirement | Real-time lookup API | Historical technographic database | Browser extension |
|---|---|---|---|
| You already have the domains | Strong fit | Works, but may be more than you need | Manual only |
| Fresh public homepage signals | Strong fit | Depends on crawl recency | Strong fit while browsing |
| Millions of prebuilt company records | Not a fit | Strong fit | Not a fit |
| Historical adoption and removal dates | Not a fit | Strong fit | Not a fit |
| Automated CRM enrichment | Strong fit | Strong fit | Weak fit |
| Evidence for each match | Depends on provider; required here | Varies | Usually visual only |
| One-off human research | Acceptable | Acceptable | Strong fit |
| Low-volume evaluation budget | 50 free requests/month here | Often expensive | Often free |
BuiltWith’s official Domain API returns technology information for
supplied websites and also supports multiple-domain requests. Its wider
commercial product includes datasets and historical context that a
lightweight checker does not attempt to recreate.
Use the StadiaSoft API when you need fresh, structured
lookups for domains you already possess. Choose a full
technographic database when the job begins with “find every company
using technology X,” or when adoption history is central to the
decision. Use an extension when a person is researching a few sites
interactively.
That distinction is the first safeguard against disappointed users.
“Alternative” should describe the overlapping job, not claim identical
coverage.
How an
evidence-backed website technology checker works
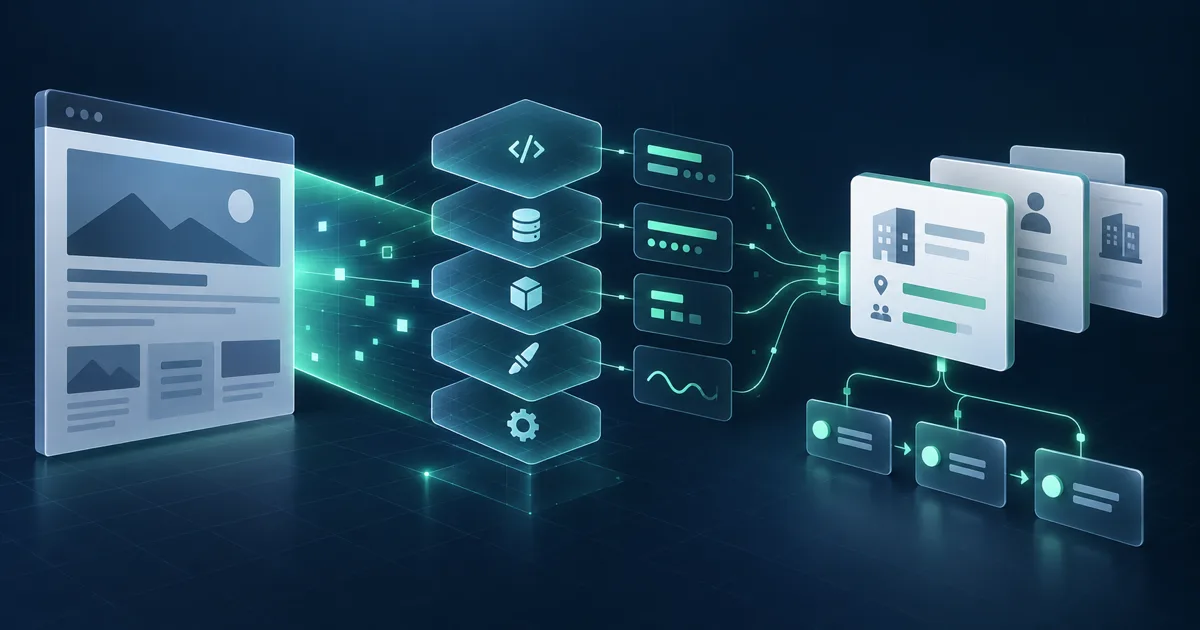
A public website exposes clues in several places:
- HTML paths such as
/wp-content/or framework-specific
root elements <meta name="generator">values- Script and stylesheet URLs
- Response headers such as
serverand
x-powered-by - Cookies with vendor-specific names
- Asset hosts and CDN domains
- Redirect destinations
One signal can be misleading. An article that mentions WooCommerce
should not cause a WooCommerce detection. A third-party widget can load
a script that resembles a platform marker. A reverse proxy can hide the
server. Reliable detection therefore needs both specific fingerprints
and an explanation of what matched.
The current StadiaSoft catalog contains 40 technologies
across 19 categories. Coverage includes CMS platforms,
ecommerce, JavaScript frameworks, UI libraries, analytics, tag
management, hosting, CDNs, web servers, marketing automation and
payments.
Every match returns:
- technology name and category
- confidence from 0 to 99
- version when a public signal exposes one
- official website
- one or more evidence objects containing the source, matched value,
explanation and per-signal confidence
The important design choice is that WordPress, 95 is not
the whole answer. The consumer can inspect whether the score came from a
generator tag, two WordPress asset paths, a cookie, or a weak text
pattern.
Make the first request from
Node.js
Node.js has included a stable browser-compatible fetch()
implementation since version 21. Keep the RapidAPI key on the server,
not in frontend JavaScript.
Copy the host from the code snippet in your RapidAPI dashboard, then
set two environment variables:
RAPIDAPI_HOST=copy-the-host-from-your-rapidapi-snippet
RAPIDAPI_KEY=your-rapidapi-application-key
The fastest lookup uses GET /detect:
const params = new URLSearchParams({
  url: "shopify.com",
  timeout_ms: "8000",
});

const response = await fetch(
  `https://${process.env.RAPIDAPI_HOST}/api/v1/technology-stack/detect?${params}`,
  {
    headers: {
      "x-rapidapi-key": process.env.RAPIDAPI_KEY,
      "x-rapidapi-host": process.env.RAPIDAPI_HOST,
    },
  },
);

if (!response.ok) {
  const errorBody = await response.text();
  throw new Error(`Technology lookup failed (${response.status}): ${errorBody}`);
}

const result = await response.json();

console.log({
  finalUrl: result.final_url,
  detected: result.summary.technologies_detected,
  categories: result.summary.categories,
  technologies: result.technologies,
});
RapidAPI authentication requires both X-RapidAPI-Key and
X-RapidAPI-Host. Never commit the key, put it in a public
URL, or paste it into a support request.
Use a JSON POST when the rest of your integration already sends a
request body:
const response = await fetch(
  `https://${process.env.RAPIDAPI_HOST}/api/v1/technology-stack/detect`,
  {
    method: "POST",
    headers: {
      "content-type": "application/json",
      "x-rapidapi-key": process.env.RAPIDAPI_KEY,
      "x-rapidapi-host": process.env.RAPIDAPI_HOST,
    },
    body: JSON.stringify({
      url: "wordpress.org",
      timeout_ms: 8000,
      force_refresh: false,
    }),
  },
);
force_refresh bypasses the five-minute response cache.
Leave it off for normal enrichment. A CRM does not need to refetch the
same domain several times within one import.
Understand the
result before automating it
The following shortened response shows the relevant shape. The domain
and matched values are illustrative, so use your live result when
writing production rules.
{
  "success": true,
  "requested_url": "https://example.com/",
  "final_url": "https://www.example.com/",
  "status_code": 200,
  "redirects": [
    "https://example.com/",
    "https://www.example.com/"
  ],
  "technologies": [
    {
      "name": "Cloudflare",
      "category": "CDN",
      "confidence": 99,
      "version": null,
      "website": "https://www.cloudflare.com",
      "evidence": [
        {
          "source": "header",
          "signal": "Cloudflare response header",
          "matched": "server: cloudflare",
          "confidence": 99
        }
      ]
    }
  ],
  "summary": {
    "technologies_detected": 1,
    "categories_detected": 1,
    "categories": ["CDN"],
    "highest_confidence": 99
  },
  "request_id": "7eea3f51-7d70-4f2f-a88e-8dd58a4d4bde"
}
Keep request_id with your enrichment log. It gives
support a precise request to trace without exposing the API key.
Do not store only the technology names. At minimum, retain the
confidence, evidence source and checked time. Otherwise a future user
cannot distinguish a strong header match from a weak pattern.
Use the Evidence
→ Confidence → Action framework
An enrichment rule should have three layers.
1. Evidence
Preserve the public signal that produced the match. Examples include
a vendor-specific header, a generator tag, two independent asset paths
or a platform cookie.
2. Confidence
Set an automation threshold. A value of 90 or above may be sufficient
for routing, while a lower score may require manual review. The exact
threshold depends on the cost of a false positive.
3. Action
Tie a confirmed category to one explicit workflow:
- Shopify or WooCommerce can route an account to the ecommerce
segment. - WordPress can trigger a CMS-migration checklist.
- HubSpot may add an integration-fit tag.
- Stripe or PayPal may enrich a payments field.
- Vercel or Netlify may route a site to a modern-hosting
sequence.
This is safer than turning every detected technology into a sales
claim. A public script indicates observable use on the checked page. It
does not prove the size of the deployment, the contract value, or
whether the tool is used throughout the company.
Normalize the result for a
CRM
CRM fields should be stable even when the API catalog grows. Store a
normalized array and derive high-level fields for segmentation.
function normalizeTechnologyResult(result) {
  const observedAt = new Date().toISOString();

  const technologies = result.technologies.map((technology) => ({
    name: technology.name,
    category: technology.category,
    confidence: technology.confidence,
    version: technology.version ?? null,
    evidence_sources: [
      ...new Set(technology.evidence.map((item) => item.source)),
    ],
    observed_at: observedAt,
  }));

  const highConfidence = technologies.filter(
    (technology) => technology.confidence >= 90,
  );

  return {
    tech_lookup_status: "complete",
    tech_checked_at: observedAt,
    tech_final_url: result.final_url,
    tech_categories: [...new Set(highConfidence.map((item) => item.category))],
    tech_names: highConfidence.map((item) => item.name),
    tech_evidence: technologies,
    tech_request_id: result.request_id,
  };
}
Keep the raw normalized array in a JSON-capable field or your data
warehouse. Put only the fields used for filters into the CRM’s top-level
properties. This prevents dozens of rarely used Boolean columns.
A practical refresh policy is also important. Website stacks do not
usually need minute-by-minute checks. Start with a lookup during account
creation, then refresh active accounts weekly or monthly. Recheck
immediately when a migration or redesign is known.
Enrich up to five
domains in one request
The bulk endpoint accepts one to five domains. Each item succeeds or
fails independently, so one unreachable site does not discard the other
results.
const response = await fetch(
  `https://${process.env.RAPIDAPI_HOST}/api/v1/technology-stack/bulk`,
  {
    method: "POST",
    headers: {
      "content-type": "application/json",
      "x-rapidapi-key": process.env.RAPIDAPI_KEY,
      "x-rapidapi-host": process.env.RAPIDAPI_HOST,
    },
    body: JSON.stringify({
      urls: [
        "wordpress.org",
        "shopify.com",
        "vercel.com",
        "example.com",
        "this-domain-should-not-exist.invalid"
      ],
    }),
  },
);

const batch = await response.json();

for (const item of batch.results) {
  if (!item.success) {
    console.warn("Lookup failed", item.url, item.error.code);
    continue;
  }

  const crmFields = normalizeTechnologyResult(item);
  console.log(item.requested_url, crmFields.tech_names);
}
For larger imports, split domains into groups of five and limit
concurrency in your own worker. Respect your plan’s monthly allowance
and overage pricing. Retry only transient fetch failures, not invalid
URLs.
Accuracy depends
on what a public page reveals
Technology detection is fingerprinting, not privileged inspection. It
can miss a tool when:
- a production build removes recognizable markers
- a reverse proxy strips headers
- scripts load only after user interaction
- the homepage does not use a tool present on an inner page
- a consent manager blocks analytics until permission is granted
- assets are proxied through the site’s own domain
- the technology is entirely backend or internal
False positives are also possible. A page can mention a product in
editorial text, embed a third-party widget or retain a stale script
after a migration. The detector therefore weighs specific public signals
and returns evidence.
Evaluate the service with a controlled set, not one impressive
demo:
- A known WordPress site with public asset paths.
- A Shopify store.
- A site deployed on Vercel with a recognizable framework.
- A custom site with few public fingerprints.
- An invalid or private hostname that must be rejected.
Record expected categories before running the test. Review mismatches
manually. If a result will trigger outreach or a customer-facing
recommendation, require high confidence and at least one specific
evidence item.
URL-fetching
services need SSRF protection
A technology detector fetches a URL supplied by a caller, so
server-side request forgery is a core risk. OWASP recommends strict URL
validation, careful redirect handling and protection against internal
network destinations.
This API accepts only HTTP and HTTPS on ports 80 and 443. It rejects
IP literals, local hostnames, private networks and reserved address
ranges. Every redirect destination is normalized, resolved and checked
again before connection. Fetches stop after five redirects and responses
are capped at 2 MB.
If you build your own detector, do not rely on a regex or one
hostname check. DNS can change between validation and connection,
alternate IP representations can bypass naive rules, and an apparently
public URL can redirect to an internal service.
Cost and
coverage: what 50 free requests can prove
The Basic plan includes 50 requests per month with
all endpoints available. That is enough for a structured evaluation:
| Test group | Domains | Purpose |
|---|---|---|
| Known CMS sites | 10 | Validate WordPress, Shopify, Drupal and related categories |
| Framework/hosting sites | 10 | Validate Next.js, React, Vercel, Netlify and CDN signals |
| Martech-heavy sites | 10 | Check analytics, tag managers and marketing automation |
| Low-signal custom sites | 10 | Measure unknown and partial outcomes |
| Repeats and failure cases | 10 | Test caching, redirects, invalid input and retry behavior |
Current paid presentation is $25/month for 1,500 requests, $75 for
7,500, and $150 for 25,000, with plan-specific overage pricing. Check
the live marketplace before budgeting because plans can change.
The detector’s catalog currently covers 40 technologies. That is
intentionally smaller than large commercial fingerprint libraries.
Choose it for explainable, real-time enrichment and a straightforward
RapidAPI subscription. Do not choose it when your requirement is an
exhaustive historical index or a list of every company using a niche
product.
Where this workflow fits
The normalized output can support several concrete processes:
- CRM enrichment: add current CMS, ecommerce,
framework, hosting and analytics fields to known accounts. - Lead routing: send Shopify and WooCommerce sites to
an ecommerce team. - Integration discovery: flag observable tools your
software connects with. - Migration prospecting: identify public platforms
that match a documented migration offer. - Account research: give sales representatives
evidence before a call. - Portfolio monitoring: compare public stack changes
across customer domains.
For trust and domain-age signals, combine the result with the Domain
Intelligence & Website Trust Score API. For sender
authentication, use the Domain
Mail Security & Deliverability Audit API. Each API should own
one clear job rather than producing an opaque master score.
BuiltWith alternative FAQ
What is a BuiltWith
alternative?
It is a tool that overlaps with one or more BuiltWith jobs, such as
identifying public website technologies, enriching supplied domains,
building technographic lists or tracking adoption. Compare the exact job
and dataset rather than assuming every alternative has the same
coverage.
Can this API
detect WordPress, Shopify and Next.js?
Yes, when their supported public signals are present. The catalog
also includes WooCommerce, Drupal, Joomla, Ghost, Magento, Webflow, Wix,
Squarespace, React, Vue.js, Nuxt, Vercel and other technologies. A
hidden or removed fingerprint can prevent detection.
Is this a Wappalyzer
alternative too?
It overlaps with Wappalyzer’s real-time website lookup use case and
returns structured API data with evidence. It does not replace
Wappalyzer’s browser extension, full commercial dataset or every
fingerprint in its library.
Does
a detection prove the company uses the product everywhere?
No. It proves that the checked public page exposed a matching signal
at that time. Preserve the evidence, apply a confidence threshold and
avoid turning a website signal into an unsupported company-wide
claim.
Can I use the API
for bulk lead generation?
You can enrich domains you already have in batches of up to five per
request. The API does not provide a prebuilt list of companies using a
technology.
Does the API render
JavaScript?
No. It inspects the public HTTP response, HTML, headers, cookies and
generator metadata. Technologies revealed only after browser-side
execution can remain undetected.
Run a five-domain evaluation
The right first test is not a random famous website. Choose five
domains whose stacks you can independently verify, define the expected
categories, and compare every match with its evidence.
Open
the CMS Checker & Website Technology Detector API on RapidAPI
and use the 50 free monthly requests to evaluate the workflow. If the
catalog matches your target technologies and the evidence is strong
enough for your automation threshold, connect the normalized output to a
small CRM segment before expanding volume.